
mokey
Self-service account management portal for FreeIPA / Red Hat IdM: signup, password reset, TOTP, passkeys, OIDC via Hydra, admin panel, group self-service with sponsor approval, and access visibility. Standalone web app using FreeIPA JSON-RPC API without LDAP schema changes.
Ficha actualizada 23 sept 2026, 17:10 · upstream 23 sept 2026, 16:54 · release v2.2.3
Qué es mokey
Descripción editorial construida a partir del repositorio, su documentación y sus señales de mantenimiento.
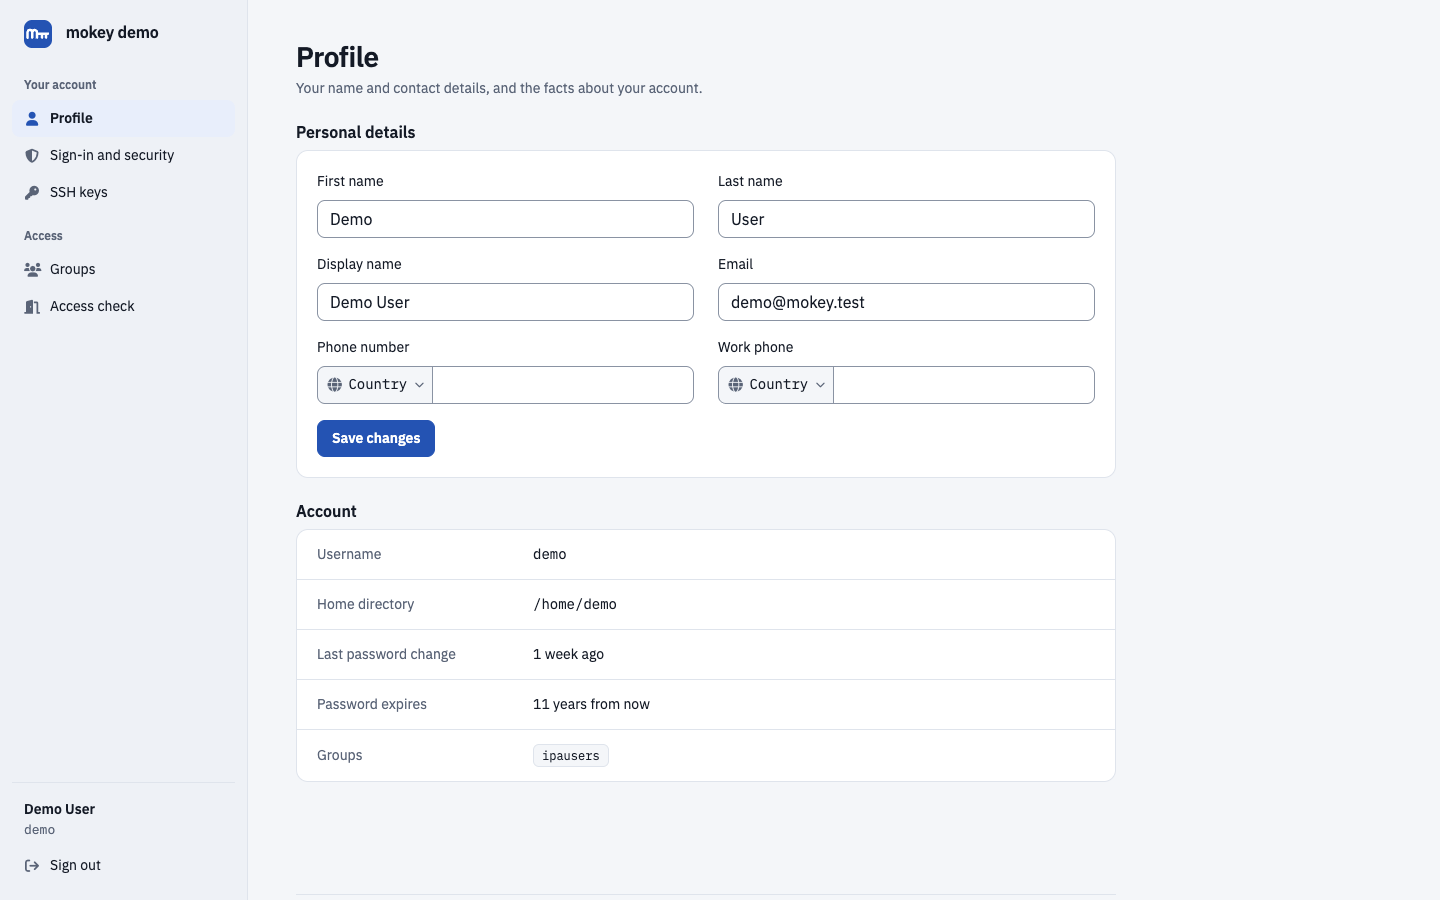
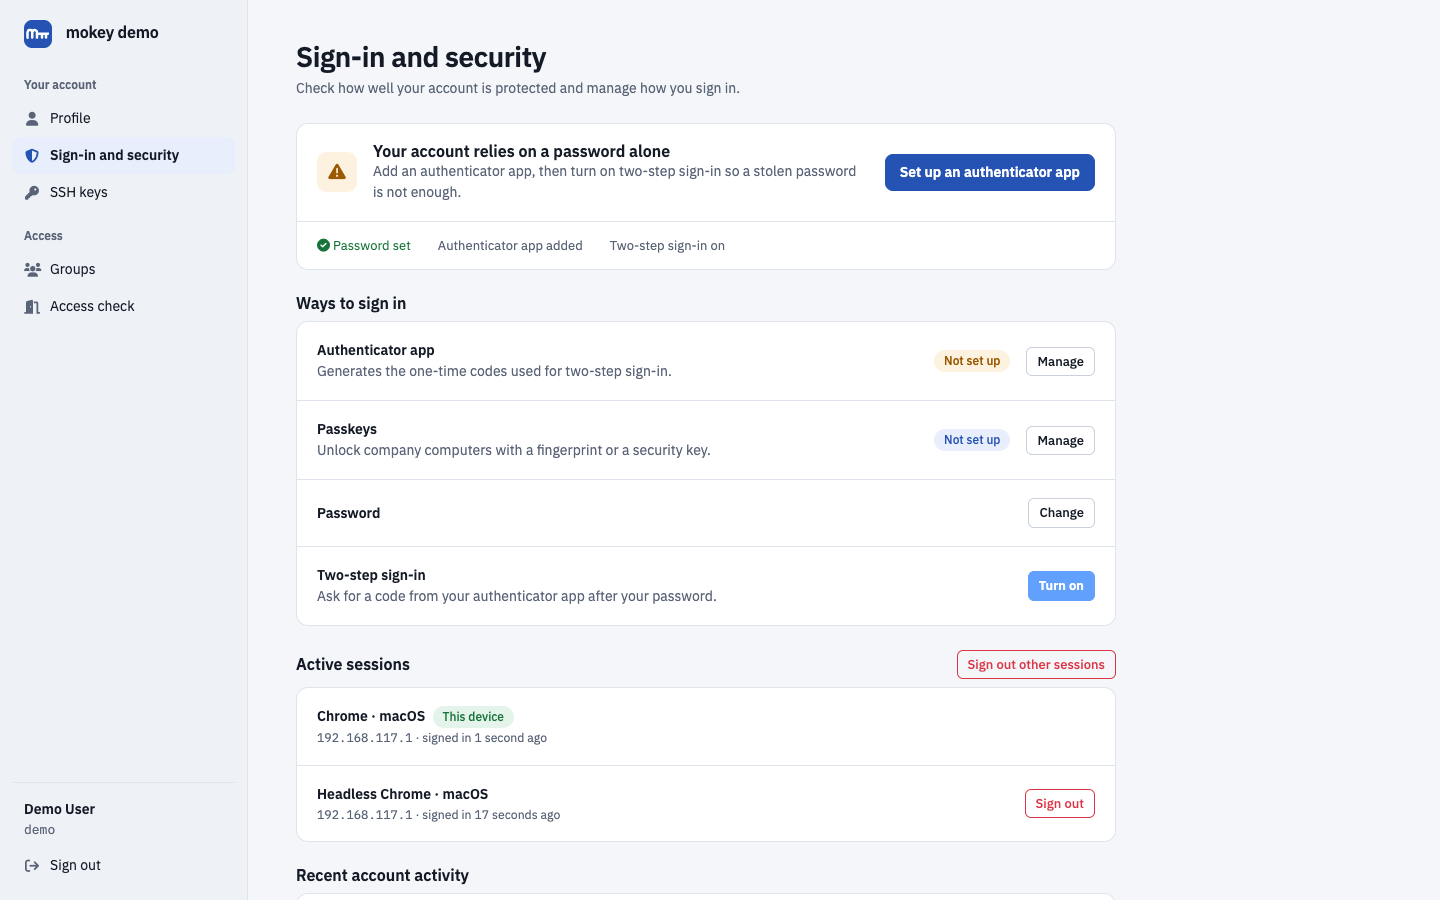
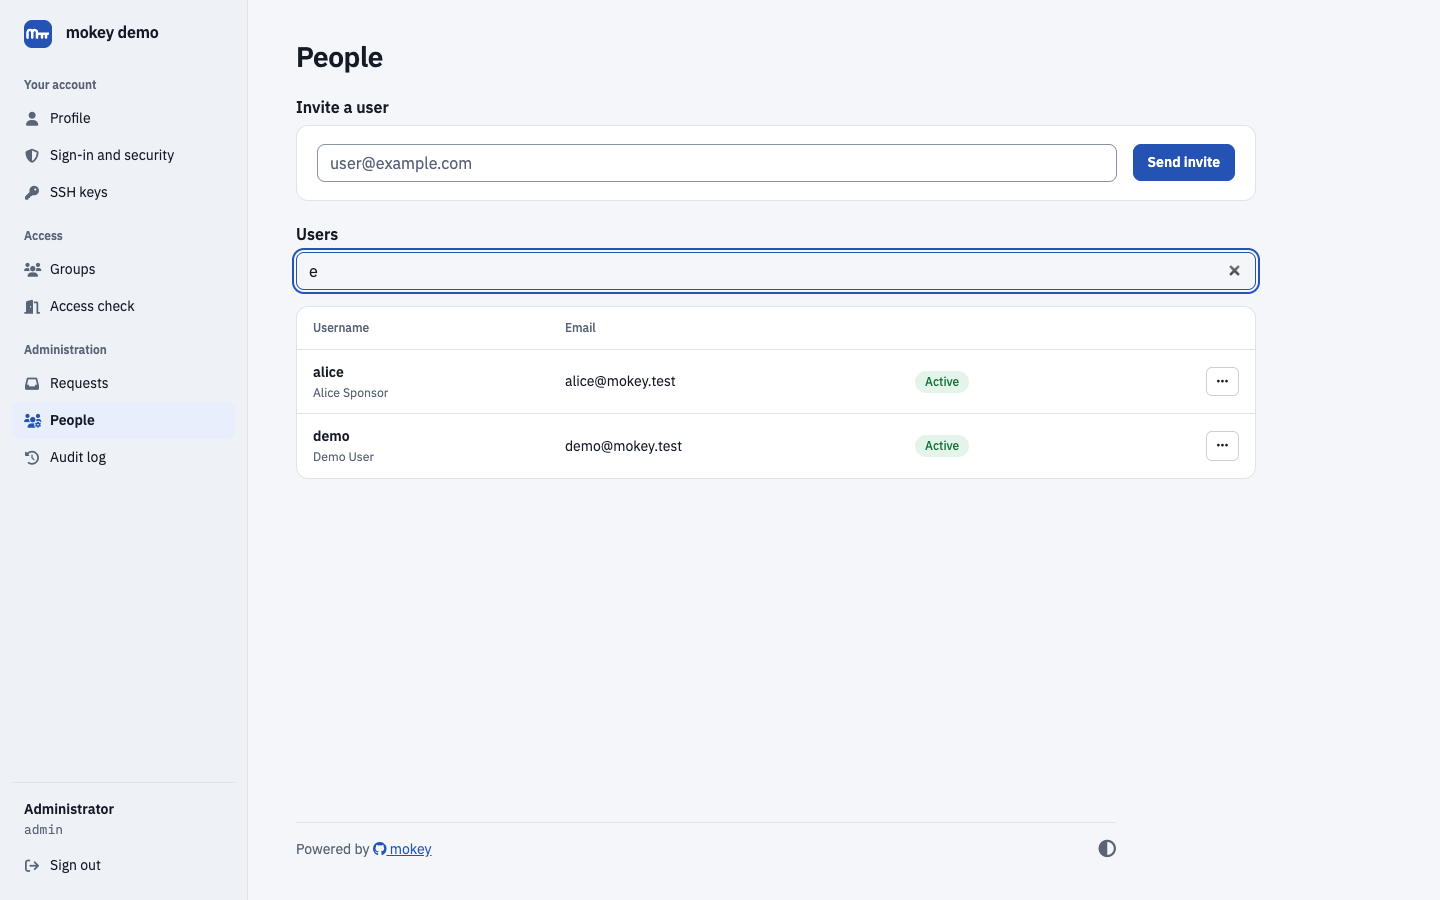
mokey provides FreeIPA users a dedicated portal for account management: signup, password change/reset, SSH keys, OTP tokens, passkeys (WebAuthn), session monitoring, group requests with sponsor approval, and access visibility via HBAC/sudo rules. It talks to FreeIPA JSON-RPC API without LDAP schema modifications, acts as login/consent provider for Ory Hydra (OAuth 2.0/OpenID Connect), keeps sessions in memory or Redis, uses least-privilege service accounts, and includes unauthenticated /healthz endpoint for load balancer health checks. Originally forked from ubccr/mokey, now independently maintained by neverlless.
- Self-service password reset for FreeIPA users without admin intervention
- SSH key management where users can add/remove keys via their account page
- Two-factor authentication (TOTP) registration and token issuance
- Passkey self-registration using WebAuthn in FreeIPA 4.11+
- Hydra OAuth/OIDC login with mokey as the consent provider for external apps
- Group-based self-service where sponsor approval is required before group membership changes
- Visibility dashboard showing which HBAC/sudo rules apply to a user's account
- OTP lockout recovery flow allowing users to request password reset after token loss
- No LDAP schema changes required — mokey uses FreeIPA service accounts and keeps sessions in memory or Redis
- Separate application architecture: mokey acts as both the login/consent provider for Hydra and a standalone account management portal
- Supports passkeys (WebAuthn) with credentials stored only within FreeIPA, not on the client device
- Slack notifications deliver account events to users via bot tokens without requiring email configuration
- Unauthenticated /healthz endpoint enables Kubernetes liveness/readiness probes and load balancer health checks
- Requires FreeIPA v4.6.8 or greater with accounts.staged_signup enabled for full self-service password reset functionality
- Passkey support is limited to FreeIPA 4.11+ only; earlier versions do not natively support WebAuthn-based passkeys
- The "what can I access" page relies on HBAC/sudo rules and may require additional configuration in FreeIPA for full accuracy
- OTP token recovery requires admin approval via the login page, which adds a single point of failure if not properly documented
Capturas del proyecto
Imágenes reales detectadas en la documentación del repositorio.
Perfil de infraestructura
Estimación inicial derivada del repositorio y de los servicios detectados.
Despliegue detectado
Qué señales reales de instalación hemos encontrado.
mokey is designed to be containerized. Use Docker Compose with Redis as the session store: docker compose -f examples/production/docker-compose.yml up -d. For Kubernetes, use the Helm chart at charts/mokey which provides CRDs for FreeIPA integration and supports RBAC. Always run mokey behind a reverse proxy (haproxy/nginx) to handle SSL termination and HTTPS redirection. The application uses systemd service management on Debian/RHEL systems with systemctl enable --now mokey to ensure persistent startup. For production, consider using the official release tarball or Docker image from ghcr.io/neverlless/mokey:latest.
Stack y dependencias
Componentes inferidos a partir de manifests, configuración y documentación.
Puede sustituir a
Relaciones detectadas por el análisis del repositorio y su categoría.
Experiencia real de la comunidad
Ayuda a contrastar la estimación automática con instalaciones reales.
Todavía no hay datos comunitarios para este proyecto.